
No-KYC VPS Hosting Providers
Review payment records and the admin path separately. XMR, Tor and hardening reduce specific exposures, not every record. Identified acquisition records can remain without a transparent public Monero trail to the invoice. The operator and physical host remain trust points.
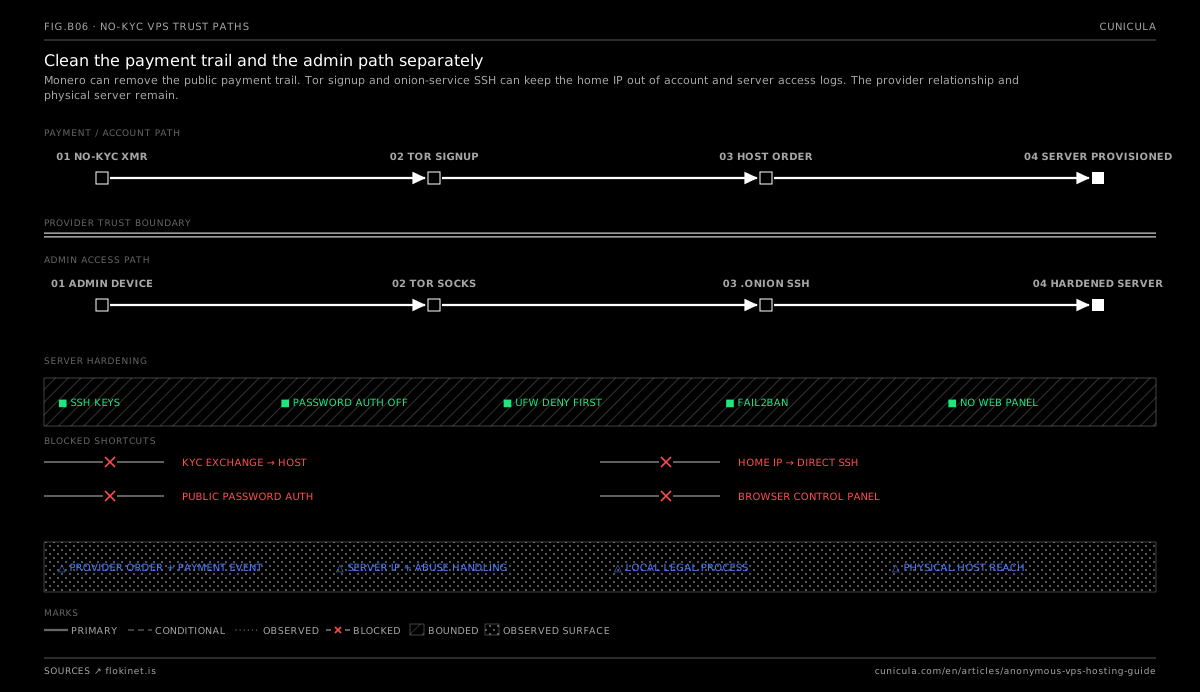
Data behind this diagram
| Stage | Control | Risk if skipped |
|---|---|---|
| Acquire payment | Check acquisition and counterparty records | Monero does not expose a transparent public trail to the invoice; identified acquisition records can remain |
| Create account | Check initial form, full terms and Tor support | Email aliases and Tor do not erase payment/contact records |
| Pay host | Follow the exact current invoice | Address, confirmations and provisioning differ by host |
| Harden SSH | Inspect sshd_config.d first-value precedence; sshd -t and -T/-C; prove a second key-only login | A main-file edit alone may not disable other authentication paths |
| Firewall | Allow actual management port, verify access, enable and inspect UFW | Provider firewalls and container networking require separate checks |
| Public SSH jail | Enable correct sshd jail/backend and verify status | Onion sessions normally appear from local Tor, not the real client IP |
| Management software | Maintain and restrict only required software | Unnecessary panels add maintenance and exposed management code |
| Onion transition | Prove a second onion session and recovery route, then remove public allow rules explicitly | Default deny does not remove earlier allow rules; host still controls VM infrastructure |
Renting a server without an identity link comes down to three records: the payment trail, the registration identity, and the admin IP in access logs. The providers accept privacy-oriented payment options, but account and billing requirements differ. Initial signup, full-service terms and the records generated by payment must be checked separately. The host still sees the server IP, abuse complaints, access times, and whatever SSH exposes, and each provider documents some logging in its own terms. Jurisdiction, account hygiene, and server hardening decide the rest.
Hosting intent: this page is for renting and hardening a server without an identity link. It is not a VPN guide. See the VPN category for IP masking, the private DNS setup guide for resolver privacy, and this guide when the need is root access to infrastructure.
- All four compared providers record Monero acceptance, which removes the public chain trail a Bitcoin payment leaves. The provider still records the order on its side.
- Compare company base and hardware location separately: 1984 and FlokiNET report Icelandic companies, Njalla a Costa Rica company with Swedish VPS hardware, and IncogNET a Wyoming company. None removes legal reach.
- Inspect the actual image, prove key-only SSH access, configure the firewall, and verify any public-SSH fail2ban jail. Keep recovery access while changing management paths.
- providers compared, all recording Monero acceptance
- 4
- Confirmed
- Source pages, reviewed 2026
- operators reporting a company base outside the US/UK
- 3
- Confirmed
- 1984 and FlokiNET: Iceland; Njalla: Costa Rica; server locations differ
- the server address the host always sees
- IP
- Caution
- Anonymous payment does not remove access logs
Jurisdiction moves the process, not the reach
Company base, server location and the law governing the particular service can all matter. The providers’ published terms reserve lawful disclosure or compliance. A foreign company or a server outside the US and UK does not by itself remove legal reach or access by the host.
Iceland is a common choice for press-adjacent hosting under its data-protection regime, and both 1984 Hosting and FlokiNET run Icelandic infrastructure. Romania, where FlokiNET also operates, sits inside the EU. Njalla reports a Costa Rica company base, but its VPS hardware is in Sweden. The physical location of the hardware matters as much as the company's: a server can be imaged or seized where it runs, whatever the incorporation says.
Provider comparison
| Provider | Company base / VPS location | XMR | Published signup limits | Documented limits |
|---|---|---|---|---|
| 1984 Hosting | Iceland / Reykjavik | Yes | Initial form: email/password, phone optional; broader contact/payment terms apply | IP/device/visit records and bookkeeping retention per policy |
| FlokiNET | Iceland / Iceland, Romania, Finland, Netherlands | Yes | Advertises email-only; policy permits supplied contact/billing data | Visit/IP/browser records, accounting and security retention per policy |
| Njalla | Costa Rica (provider-reported) / Sweden | Yes | Email or XMPP and password | Domain terms are not a complete VPS-specific data policy |
| IncogNET | Wyoming, US / multiple locations | Yes | Email aliases allowed; account/payment records | IP/security records; all VPS locations sold out at 8 November check |
1984 Hosting runs from Reykjavik and its record documents Monero acceptance alongside Bitcoin. Its published policy covers IP/device/visit records and supplied account information. The initial form asks for email/password and optional phone, while its terms describe broader subscriber contact and payment details; do not read no document upload as a guarantee of no identity data. Iceland is its jurisdiction for both company and infrastructure.
FlokiNET operates across Iceland, Romania, Finland, and the Netherlands with Monero accepted. Its privacy policy permits supplied billing/contact data, visit/IP/browser records, seven-year accounting retention and potentially indefinite access/security records. Its VPS page describes SSH-key-only provisioning; verify the actual image and recovery console rather than assuming defaults.
Njalla is better known for proxy domain registration and also sells VPS plans, with Monero accepted. Signup uses an email or XMPP address. Njalla reports a Costa Rica company base, while its VPS page places the servers in Sweden. Holding the domain and server under one account concentrates both records with one operator.
IncogNET permits email aliases and accepts Monero under a Wyoming company. Its policy allows account, payment, IP and security records. Its VPS page showed all locations sold out when checked on 8 November 2026; check current availability before ordering. Payment privacy does not remove the operator’s account records or applicable law.
Monero removes the public payment trail
Bitcoin is transparent: every transaction stays on a public ledger, and chain-analysis can connect a payment from an identified wallet to a hosting invoice. Monero does not produce a publicly readable record, because ring signatures, stealth addresses, and confidential amounts apply to every transaction. All four providers here record Monero acceptance. The provider still logs the order and payment event on its own side, so the improvement is the public chain trail, not the provider relationship.
Check the current invoice for payment detection, confirmation requirements and provisioning time. These are separate steps and can differ by provider.
Check XMR acquisition records
Review what the acquisition service and payment counterparty collect before obtaining XMR. Haveno is non-KYC peer-to-peer software, but live networks are operated by third parties and the payment method can disclose information. Swaps, ATMs and identified exchanges each have their own records and exceptions; none is an automatic anonymity guarantee.
Create the host account over Tor
Where supported, open the provider through Tor Browser or its official onion address. A dedicated email alias can reduce reuse, but the forwarding provider still has records. Tor changes the signup network path; it does not erase email, payment or service records.
Send XMR and wait for confirmations
Use the exact payment address and instructions on the current invoice; address handling can differ by host. Send from Feather Wallet or another Monero wallet. Check payment detection, confirmation and provisioning requirements separately. Monero hides sender, recipient and amount from ordinary public-ledger inspection. The payment still has a transaction record, and the host can associate the invoice with what it receives.
Hardening the server matters as much as paying for it
Anonymous payment means very little if the server falls to weak defaults. Inspect the actual image before relying on its defaults. Some providers deploy SSH-key-only access, while firewall and service exposure vary. The steps below assume a Debian/Ubuntu-style host; keep a tested console or recovery route before changing access.
SSH keys. Kill password auth.
Generate an Ed25519 or 4096-bit RSA key pair locally and install only the public key in the intended user’s ~/.ssh/authorized_keys. Prove a key login works before changing authentication. Keep that session and a tested provider console open.
Inspect /etc/ssh/sshd_config and /etc/ssh/sshd_config.d/*.conf. Ubuntu/Debian commonly include drop-ins near the top; for most directives the first obtained value wins. A cloud-init drop-in can override a later main-file edit. Change the effective owner or remove the conflict. For a key-only setup use PubkeyAuthentication yes, PasswordAuthentication no, KbdInteractiveAuthentication no and AuthenticationMethods publickey. Preserve an intentional second-factor model instead if required. PermitRootLogin prohibit-password still permits root keys; use a tested non-root sudo account before setting it to no.
Run sshd -t to validate syntax, then sshd -T to inspect PasswordAuthentication, KbdInteractiveAuthentication, PubkeyAuthentication, PermitRootLogin, AuthenticationMethods and UsePAM. Use sshd -T -C user=USER,host=HOST,addr=CLIENT_IP with the real connection values to check Match blocks. Reload ssh on Ubuntu or the distribution’s sshd service only after validation. Prove a second key-only login succeeds before closing the original session.
UFW firewall. Deny first.
Install UFW (apt install ufw). Set the defaults with ufw default deny incoming and ufw default allow outgoing. Allow SSH with ufw allow 22/tcp only if 22 is your actual management port; otherwise substitute the configured port. Prove a second SSH connection first. If you run a web server, allow 80/tcp and 443/tcp. Then run ufw enable and inspect ufw status verbose and ufw status numbered. Check provider firewalls and container-managed networking separately; UFW defaults alone do not establish every path is closed.
fail2ban hits back at scanners
Install fail2ban (apt install fail2ban). Enable and configure an sshd jail in a local override, using the correct port and log backend (systemd may be needed without an auth log). Upstream defaults are five failures within ten minutes and a ten-minute ban, but distribution settings can differ and upstream jails start disabled. Check fail2ban-client status sshd after loading the configuration. IP banning addresses public SSH: onion-forwarded sessions normally reach sshd from the local Tor process, so fail2ban cannot see or ban the real client IP on that path.
No panel software
Install only management software you need and can maintain. A browser-based panel adds web code, credentials and update obligations; restrict its access if required. For a small server, SSH alone can reduce the exposed management surface.
Use a Tor hidden service for admin access
A direct public SSH connection can expose your client IP in the server's logs. An onion service changes that path: sshd normally sees the local Tor process instead of the real client IP. This does not prevent a compromised endpoint or malicious host from observing activity or identifying data you disclose in the session.
To configure SSH over Tor on the server, install Tor and add an onion service. This example assumes sshd listens on loopback port 22; verify the listener and substitute its actual port before testing. The first port is the onion service's virtual port:
Restart Tor. The .onion hostname appears in /var/lib/tor/ssh_hidden_service/hostname. To connect from your machine, route SSH through a running local Tor SOCKS proxy. This example assumes OpenBSD netcat and a proxy on port 9050; use your actual proxy port:
Keep the existing access route while testing a second SSH session over the onion service. Once it works and you have a recovery route, remove the earlier public SSH allow rule and verify the firewall. The host still knows the VM’s public IP and controls the underlying infrastructure; onion SSH protects the admin network path, not against a malicious host.
Use ufw status numbered to identify and explicitly delete the public management-port allow rule, including its IPv6 counterpart where present. Recheck the rules and prove public SSH is blocked while the onion session works. Default deny does not cancel an existing allow rule. Anyone knowing the onion address can reach it unless Tor client authorization is configured; retain SSH authentication.
What to avoid
- Assuming XMR erases acquisition records: the exchange may retain identified acquisition and withdrawal records. Monero does not expose a transparent public chain to the later invoice; counterparties, timing, network data or disclosed payment proofs can still create links. Review the limits in the Monero buying guide.
- Unnecessary browser control panels: restrict and patch any panel you require; removing unnecessary management software reduces maintenance and exposure.
- Registering from a home IP because the provider's access logs, which its terms say it keeps, then tie the account to that connection. Use Tor for signup.
- Treating jurisdiction as immunity because every provider here documents logging and lawful-disclosure terms. The choice reduces routine exposure; it does not defeat targeted legal process.
Why the offshore market exists
Compare the specific operator’s signup fields, payment records, data policy, server locations, available stock and support model. Privacy-oriented hosting still creates an operator relationship, and a smaller or foreign host does not by itself establish stronger security.
- Signup
- Check the actual initial form and full-service terms separately; no document upload does not mean no identifying data.
- Operator
- Read supplied contact/billing data, IP/security retention, company base and physical server location for the chosen service.
- Payment
- Monero removes the public chain trail; the provider records the order and payment event regardless.
- The residual
- The server IP, access logs, and abuse handling exist at every provider. Hardening and admin-over-Tor address the admin path, not the provider’s records.
Sources
Reviewed 8 November 2026. Provider policies describe published practices, not independently measured runtime logging.
- 1984 Hosting: initial signup, full-service terms, data policy and VPS prices/payment options
- FlokiNET: signup description, company contact, locations and key-only provisioning, payment methods and data and retention policy
- Njalla: payments and onion site, Costa Rica operator, Swedish VPS hardware, signup and published terms
- IncogNET: account, payment and IP/security policy and VPS stock observed sold out on 8 November
- Monero: public-ledger privacy and payment records and proofs; Haveno: software versus third-party networks
- OpenSSH: authentication, Include and first-obtained values; Ubuntu: UFW configuration; fail2ban: upstream jail defaults
- Tor Project: onion service setup and client authorization
Information is provided for educational purposes. Always verify provider terms. Not financial advice. Commercial disclosure.
Frequently Asked Questions
Can a VPS be rented without identity documents?
Some providers advertise email-only signup and accept cryptocurrency, but no-document signup does not guarantee an account without identifying records. 1984’s initial form and its broader terms differ; FlokiNET’s privacy policy also permits supplied billing/contact data. Check the signup form, service terms, payment method, IP logs and abuse records together.
Which pay with Monero?
FlokiNET, Njalla, IncogNET, and 1984 Hosting all record Monero acceptance. Monero removes the public chain trail that a Bitcoin payment leaves; the provider still records the order and payment event on its side.
Does jurisdiction remove legal reach over a server?
No. Company base, server location and service terms can involve different legal systems. Njalla reports a Costa Rica company base but places VPS hardware in Sweden; FlokiNET is an Icelandic company with several server locations. Providers reserve lawful compliance. A foreign company does not put a physical server beyond legal reach.